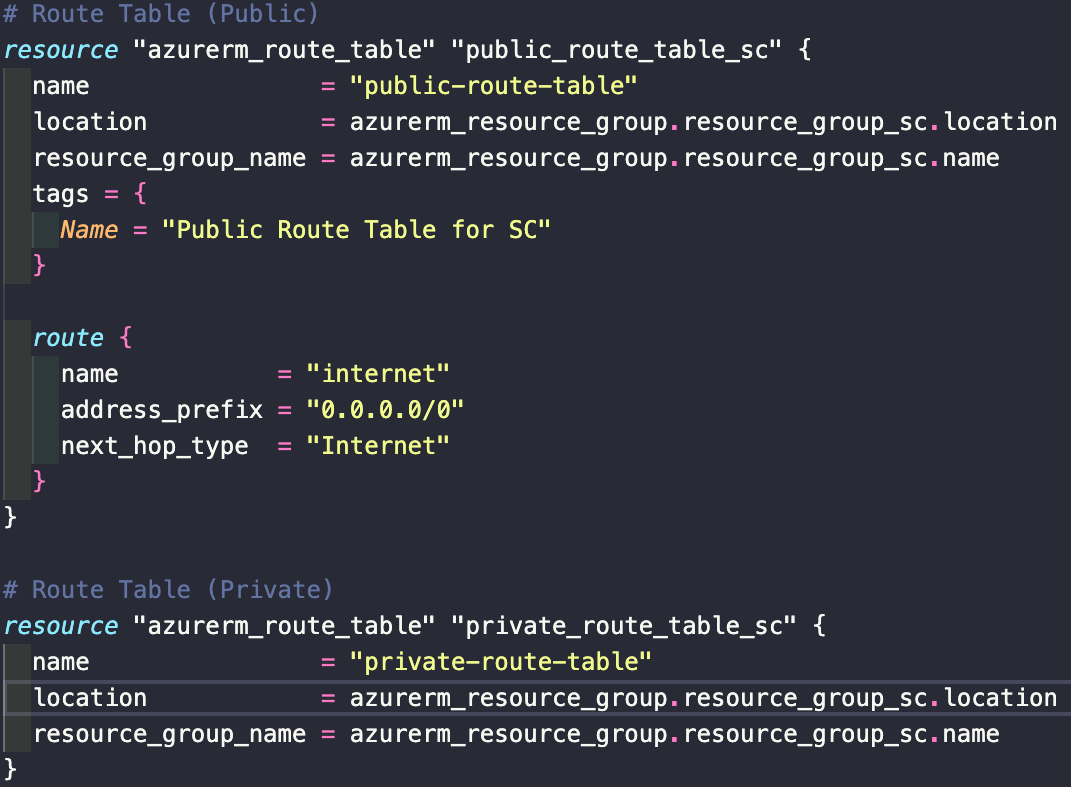
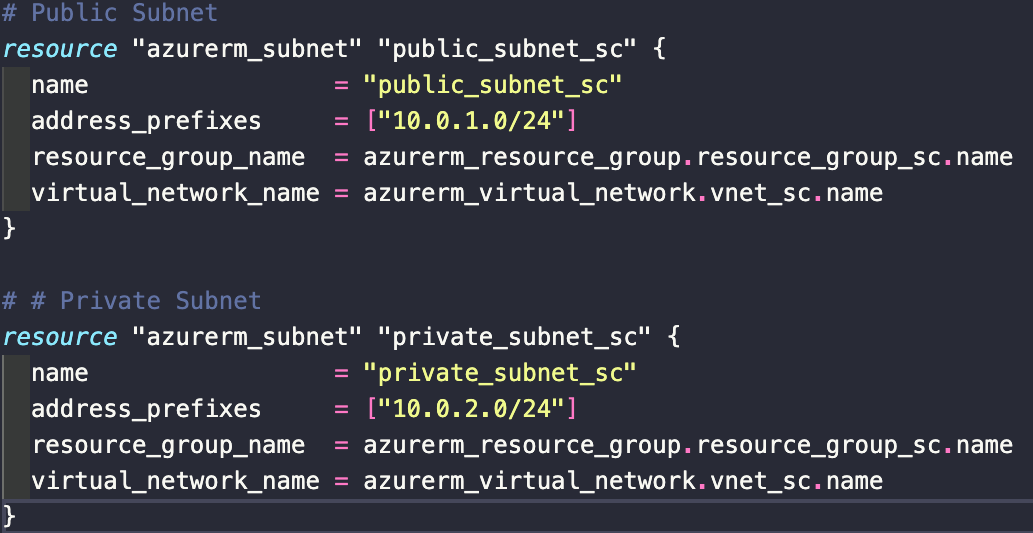
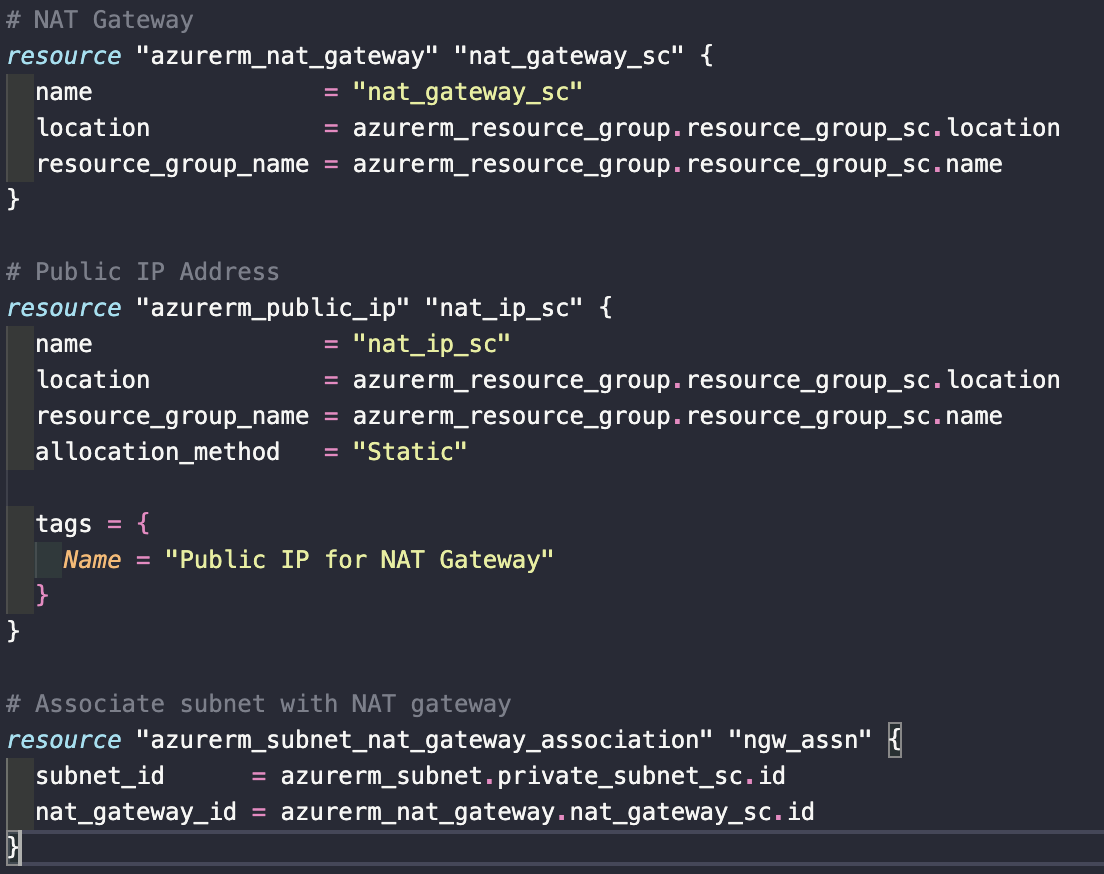
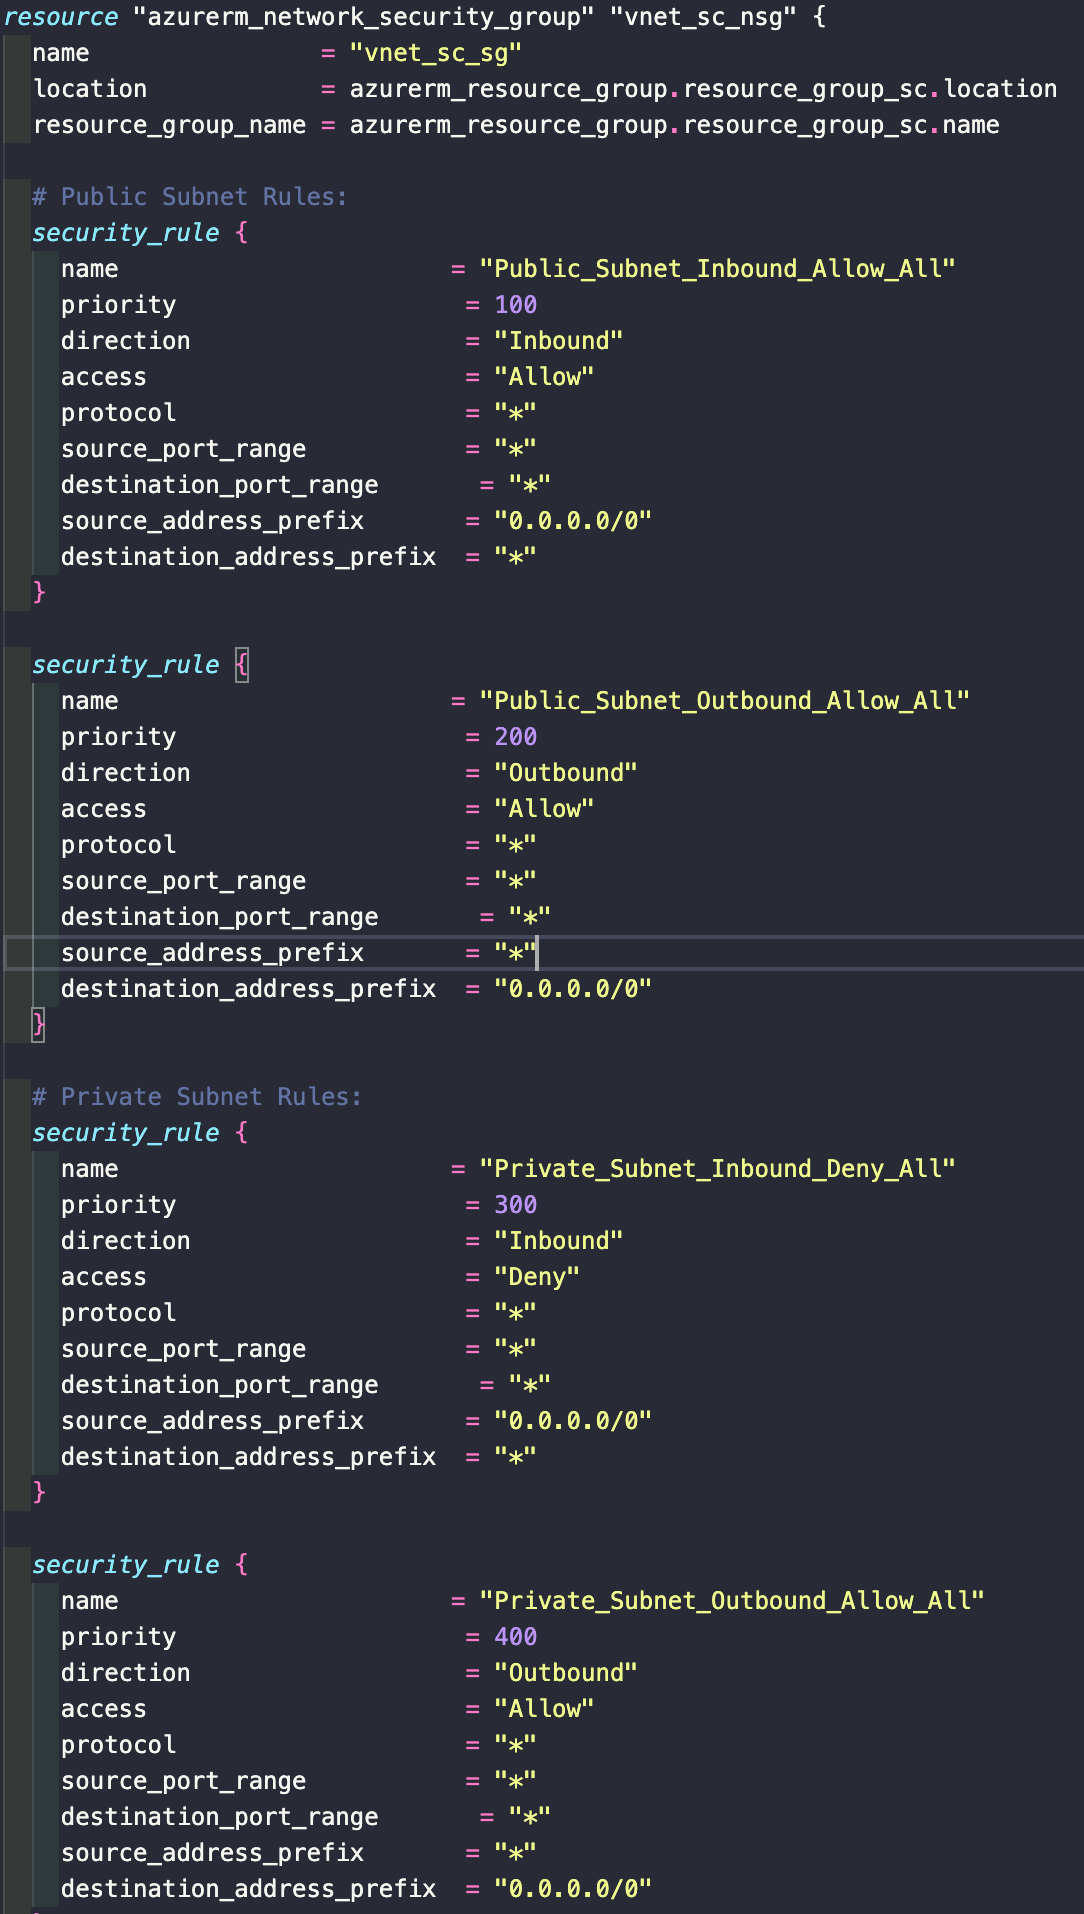
This is an Azure Virtual Network (VNet) with public and private subnets set up using Terraform. This setup provides a secure and scalable network with internet access possible for both public and private instances.
Resources created include public and private subnets, route tables, an internet gateway, a NAT gateway and security groups to ensure a secure and scalable network environment, well-structured and ready for deployment.

Services Used
Steps Taken
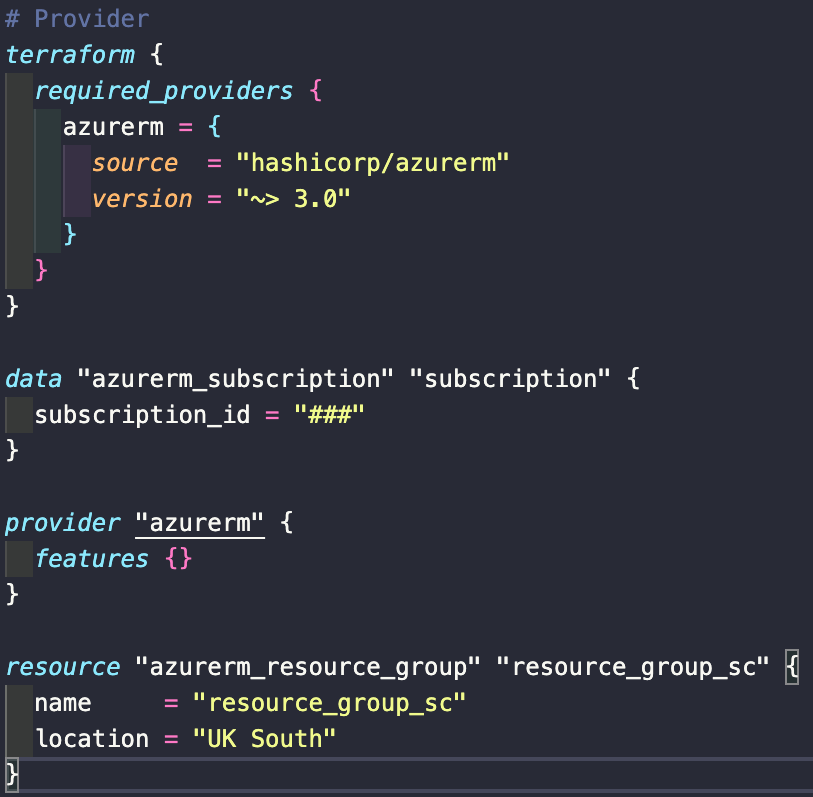
i. Each resource in Azure must belong to a resource group. A resource group is a logical container that associates multiple resources so you can manage them as a single entity, based on lifecycle and security.
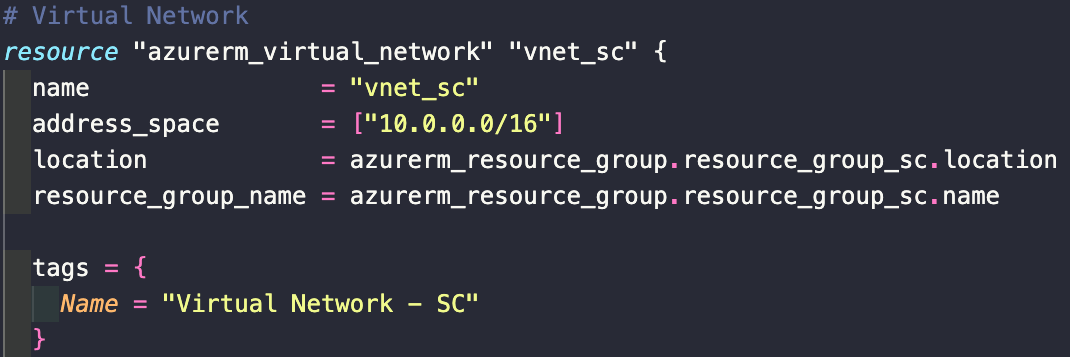
ii. When creating a private network, you must use a CIDR block from within the ranges of IP addresses reserved for private networks. 10.0.0.0/16 is within the ranges, and allows for upto 65,536 IP addresses.
iii.